CoreWeave Shares Drop After Forecast Sparks Growth Fears | Bloomberg Tech 5/8/2026
Source: Youtube
CoreWeave Shares Drop After Forecast Sparks Growth Fears | Bloomberg Tech 5/8/2026
Source: Youtube
Fmr CDC Director of infectious diseases, explains what you need to know about the hantavirus
Source: Youtube
MacBook Ultra + 3 More Macs?! What Apple Might Launch Next
Source: Youtube
What the new UFO files released by the Pentagon actually revealed
Source: Youtube
GOP Breaks Up Tennessee’s Only Majority-Black Congressional District, to Protests
Source: Youtube
'Extraordinary': Ret. admiral reacts to declassified UFO docs
Source: Youtube
IBL News | New York
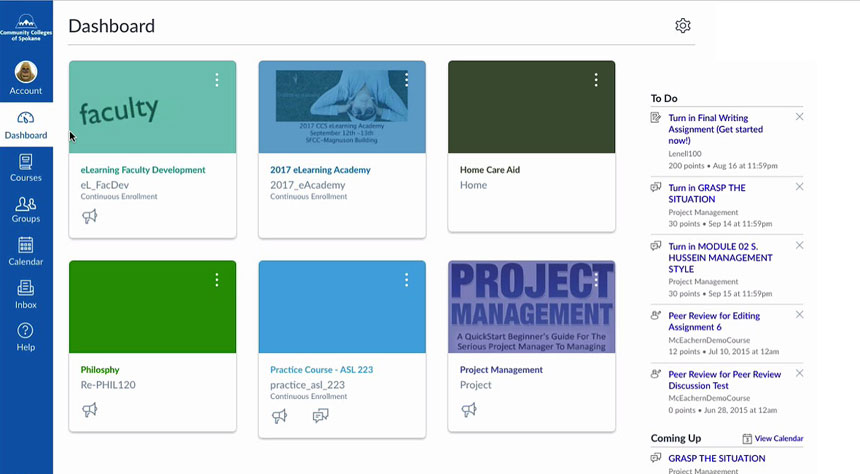
Instructure, the educational technology company behind the leading LMS, Canvas (used by 41% of higher education institutions across North America), acknowledged a security breach after the infamous ShinyHunters extortion group accessed the system and stole 3.65 terabytes of data, including personal information such as names, email addresses, and student ID numbers.
Nearly 9,000 schools worldwide (including a mix of higher education and K–12 institutions) and information of 275 million people, including students, teachers and staff, were compromised.
The hackers added the data to their Tor-based leak site. The cyberattack, which took place on April 30, was executed by “a disruption to tools relying on API keys.” Instructure disclosed the data breach on May 3, when access to the Canvas Data 2 platform was restored.
“We are working quickly to understand the extent of the incident and actively taking steps to minimize its impact,” the Salt Lake City-based company admitted.
However, “at this time, we have found no evidence that passwords, dates of birth, government identifiers, or financial information were involved,” the company said.
The ShinyHunters criminal group also claimed that Instructure’s Salesforce instance was compromised.
The hackers, who have also attacked individual universities, demanded that the ed-tech giant pay up or face a data leak.
ShinyHunters wrote in a ransom letter published May 3 by the website Ransomware.live, “to reach out by 6 May 2026 before we leak along with several annoying [digital] problems that’ll come your way,” warning the company to “make the right decision” to avoid becoming “the next headline.”
Instructure did not respond to medias’ requests for comment on the ransom and other specific questions about the attack.

Arm Warns of Phone Market Weakness | Bloomberg Tech 5/7/2026
Source: Youtube

WHO expert says that Hantavirus is 'not the next Covid'
Source: Youtube

Google’s Got Glasses Coming: What We Expect From Google IO
Source: Youtube